UTC / SOURCE AND TIME AUTHORITY MATTER
One disclosure, several clocks
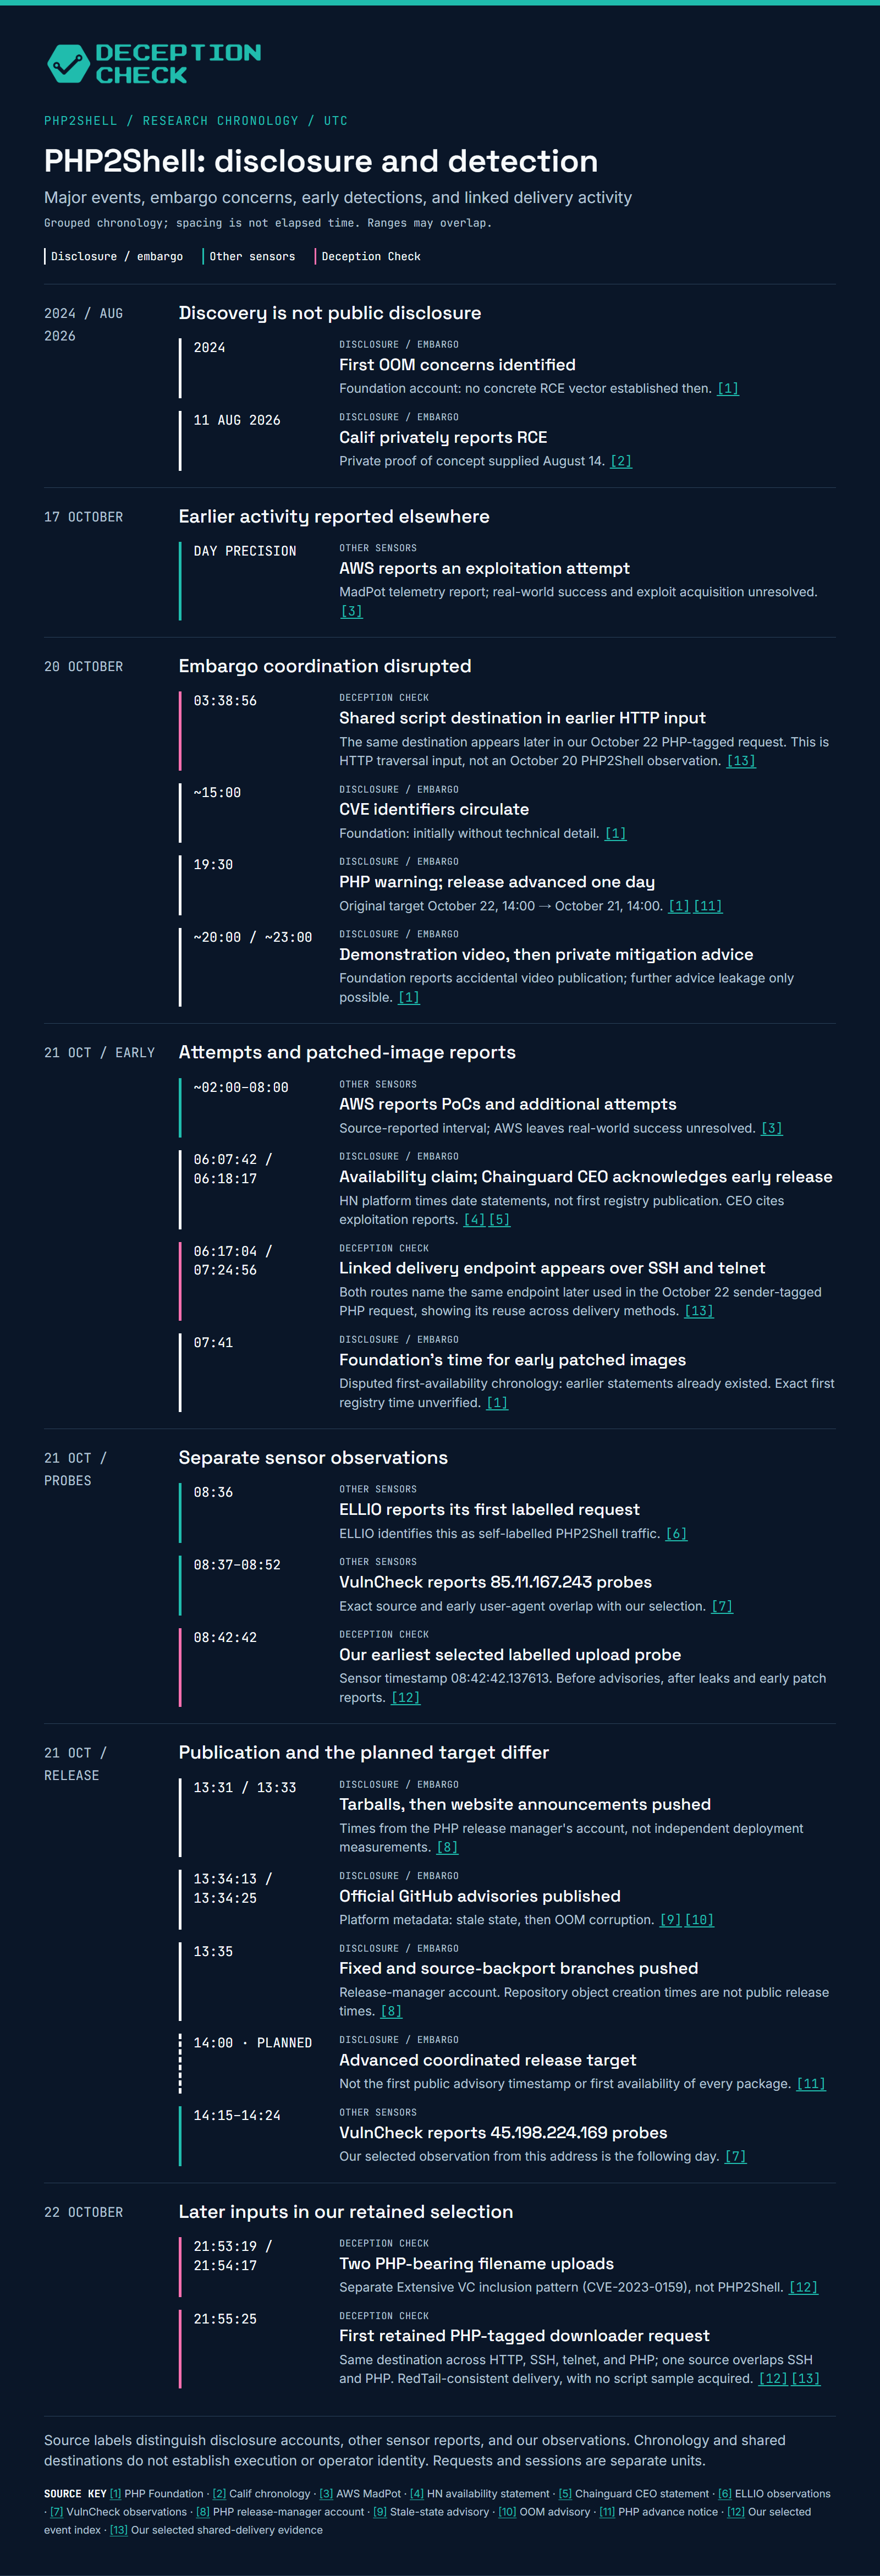
Follow the wider incident from discovery to disclosure, then compare the separate sensor reports. Each entry names its source and the kind of timestamp it provides. Early Chainguard first-availability timing remains unresolved.
PHP2SHELL / RESEARCH CHRONOLOGY / UTC
PHP2Shell: disclosure and detection
Major events, embargo concerns, early detections, and linked delivery activity
Grouped chronology; spacing is not elapsed time. Ranges may overlap.
Earlier activity reported elsewhere
- DAY PRECISIONOTHER SENSORSAWS reports an exploitation attempt
MadPot telemetry report; real-world success and exploit acquisition unresolved. [3]
Embargo coordination disrupted
- 03:38:56DECEPTION CHECKShared script destination in earlier HTTP input
The same destination appears later in our October 22 PHP-tagged request. This is HTTP traversal input, not an October 20 PHP2Shell observation. [13]
- ~15:00DISCLOSURE / EMBARGOCVE identifiers circulate
Foundation: initially without technical detail. [1]
- 19:30
- ~20:00 / ~23:00DISCLOSURE / EMBARGODemonstration video, then private mitigation advice
Foundation reports accidental video publication; further advice leakage only possible. [1]
Attempts and patched-image reports
- ~02:00–08:00OTHER SENSORSAWS reports PoCs and additional attempts
Source-reported interval; AWS leaves real-world success unresolved. [3]
- 06:07:42 / 06:18:17
- 06:17:04 / 07:24:56DECEPTION CHECKLinked delivery endpoint appears over SSH and telnet
Both routes name the same endpoint later used in the October 22 sender-tagged PHP request, showing its reuse across delivery methods. [13]
- 07:41DISCLOSURE / EMBARGOFoundation's time for early patched images
Disputed first-availability chronology: earlier statements already existed. Exact first registry time unverified. [1]
Separate sensor observations
- 08:36OTHER SENSORSELLIO reports its first labelled request
ELLIO identifies this as self-labelled PHP2Shell traffic. [6]
- 08:37–08:52OTHER SENSORSVulnCheck reports 85.11.167.243 probes
Exact source and early user-agent overlap with our selection. [7]
- 08:42:42DECEPTION CHECKOur earliest selected labelled upload probe
Sensor timestamp 08:42:42.137613. Before advisories, after leaks and early patch reports. [12]
Publication and the planned target differ
- 13:31 / 13:33DISCLOSURE / EMBARGOTarballs, then website announcements pushed
Times from the PHP release manager's account, not independent deployment measurements. [8]
- 13:34:13 / 13:34:25
- 13:35DISCLOSURE / EMBARGOFixed and source-backport branches pushed
Release-manager account. Repository object creation times are not public release times. [8]
- 14:00 · PLANNEDDISCLOSURE / EMBARGOAdvanced coordinated release target
Not the first public advisory timestamp or first availability of every package. [11]
- 14:15–14:24OTHER SENSORSVulnCheck reports 45.198.224.169 probes
Our selected observation from this address is the following day. [7]
Later inputs in our retained selection
- 21:53:19 / 21:54:17DECEPTION CHECKTwo PHP-bearing filename uploads
Separate Extensive VC inclusion pattern (CVE-2023-0159), not PHP2Shell. [12]
- 21:55:25
Open the full-resolution timeline image · Expanded chronology and sources
Expanded source ledger
Download timeline JSON · All 26 selected request records
Swipe the timeline horizontally to read event details and source links.
| Time UTC | Event and evidence type | Scope and source |
|---|---|---|
| 2024 (exact date unspecified) | First signs of the OOM problem found discovery account | Theoretical exploitation concern then, not a demonstrated RCE vector left knowingly unfixed. Source year, Foundation account |
| 2026-08-11 | Calif reports initial RCE third-party account | Private vulnerability reporting, not public exploit publication. Source day, researcher account |
| 2026-08-14 | Calif supplies private RCE proof of concept third-party account | PHP confirmation reported August 15. Source day, researcher account |
| 2026-10-17 | AWS reports an exploitation attempt third-party telemetry | AWS leaves real-world success and exploit acquisition unclear. Source day, AWS telemetry report |
| 2026-10-20 03:38:56.597539 | Shared script destination in earlier HTTP input first-party shared-delivery observation | HTTP traversal input names the same destination later submitted in our October 22 sender-tagged PHP request. The connection is the destination, not evidence of PHP2Shell use on October 20. Source microsecond string, sensor-recorded |
| 2026-10-20 ~15:00 | CVE identifiers circulate disclosure account | Initial leak described as nontechnical. Source approximate, Foundation account |
| 2026-10-20 19:30 | PHP warning; release advanced by one day disclosure account | New target October 21, 14:00; original October 22, 14:00. Source minute, Foundation account |
| 2026-10-20 ~20:00 | Accidental demonstration video disclosure account | Limited technical details; copies reportedly circulated. Source approximate, Foundation account |
| 2026-10-20 ~23:00 | Mitigation guidance shared privately disclosure account | Possible further leakage, not established. Source approximate, Foundation account |
| 2026-10-21 ~02:00 to 08:00 | AWS reports PoCs and more attempts third-party telemetry | None of its six published source IPs matches our selected five. Source approximate, AWS account |
| 2026-10-21 06:07:42 | Public comment reports patched-image availability timestamped statement | Dates the statement, not first registry publication or image contents. Source second, HN platform metadata |
| 2026-10-21 06:17:04.639046 | Linked delivery endpoint appears over SSH first-party shared-delivery observation | This SSH input names the same endpoint later used in the October 22 sender-tagged PHP request. The time marks the first retained vector-bearing curl fragment; the preceding host-bearing SCP fragment is 06:17:04.630082. Across the selected evidence window: 21 loader sessions from 2 sources, not 21 proven executions. Source microsecond string, sensor-recorded |
| 2026-10-21 06:18:17 | Chainguard CEO acknowledges early release first-party statement | Cites exploitation reports; underlying evidence not supplied there. Source second, HN platform metadata |
| 2026-10-21 07:24:56.429853 | Linked delivery endpoint appears over telnet first-party shared-delivery observation | This telnet input names the same endpoint later used in the October 22 sender-tagged PHP request, extending the linked activity across delivery methods. Across the selected evidence window: 16 loader sessions from 15 sources. Parser-split input is not proof of execution. HTTP requests and SSH/telnet sessions are different units and must not be summed as attacks or infections. Source microsecond string, sensor-recorded |
| 2026-10-21 07:41 | Foundation's time for early Chainguard images disputed first-availability chronology | Earlier statements predate this. First registry publication remains unverified. Source minute, Foundation account |
| 2026-10-21 08:36 | ELLIO reports its first labelled request third-party telemetry | Self-labelled PHP2Shell request. No exact source-IP overlap with our selected cohort established here. Source minute, ELLIO telemetry report |
| 2026-10-21 08:37 to 08:52 | VulnCheck sees 85.11.167.243 probes third-party telemetry | Exact source and early user-agent overlap with our selection. Source minute, VulnCheck telemetry report |
| 2026-10-21 08:42:42.137613 | Our first selected labelled upload probe first-party observation | 85.11.167.243; body retained as capture placeholder, not exploit validation. Source microsecond string, sensor-recorded |
| 2026-10-21 13:31 | Public release tarballs pushed release-manager account | Push chronology attributed to Daniel Scherzer; activity views not independently retrieved. Source minute, release-manager account |
| 2026-10-21 13:33 | Website announcement repository pushed release-manager account | Not an exact independent measurement of php.net deployment. Source minute, release-manager account |
| 2026-10-21 13:34:13 | Stale-state advisory published platform publication metadata | 4h51m30.862387s after our first selected request. Source second, GitHub published_at |
| 2026-10-21 13:34:25 | OOM advisory published platform publication metadata | 4h51m42.862387s after our first selected request. Source second, GitHub published_at |
| 2026-10-21 13:35 | Fixed and backport branches pushed release-manager account | Git object author/tag dates are not first-publication evidence. Source minute, release-manager account |
| 2026-10-21 14:00 | Advanced coordinated release target planned event | Do not substitute this deadline for exact advisory or package publication. Source scheduled deadline |
| 2026-10-21 14:15 to 14:24 | VulnCheck sees 45.198.224.169 probes third-party telemetry | Our selected request from this address is the next day, not this same event. Source minute, VulnCheck account |
| 2026-10-22 21:53:19.178708 and 21:54:17.455252 | Our two filename-injection uploads first-party observation | Separate Extensive VC inclusion pattern using options[template], documented as CVE-2023-0159. Not PHP2Shell. Source sensor-recorded |
| 2026-10-22 21:55:25.787307 | First retained PHP-tagged downloader request first-party observation | Same delivery host/path as earlier HTTP, SSH, and telnet inputs. Source 77.90.185.20 also appears in SSH. This dates our retained observation, not the first adoption of the vector. The delivery pattern is RedTail-consistent; the script was not retrieved. Source sensor-recorded |
Source notes: tarball/site/branch times are attributed to the release manager. Public activity views could not be independently retrieved. A Git commit or tag creation date is not a release timestamp. Our timestamp precision is the stored sensor string, not demonstrated measurement accuracy.